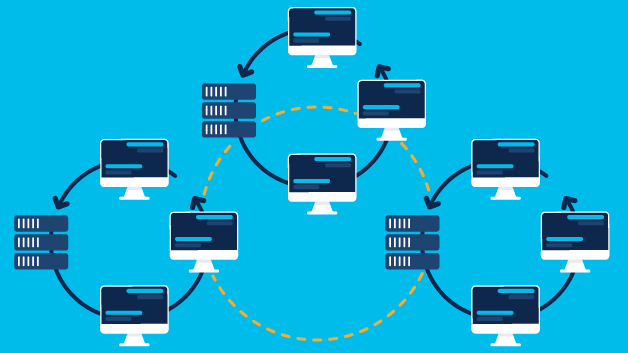
Physical routers are necessary to connect to WAN Networks. The architecture builds on established infrastructure to produce a device that is inherently lean, reusable and scalable. In this implementation, the WANs are wired directly to data center nodes and therefore have zero configuration/deployment overhead. You can find more info here.
We’ve discussed in the past how to implement a scalable WAN infrastructure in Cisco routers. While those standard configurations work for basic corporate environments, networks managing continuous high-throughput transactional loads (such as backend server clusters for forex trading platforms and tether casinos) frequently demand strict traffic segmentation. Part of this lesson looks at how to extend the set of the available features in existing routers to include 802.1Q and the 802.1Q model of IEEE 802.15.4.
Implementing 802.1Q on Cisco Routers
You’ll need a Cisco router to implement 802.1Q, and with the right process this device can be straightforward to set up. Let’s look at one way of performing this configuration.
Use the admin mode on the router to change the following items:
Administrative name
Server name (IP)
Virtual server type (Managed/Wireless/Static)
Virtual server config parameters
Turn off the WAN Bridge service and turn off the WAN Bridge checkbox.
We’ll create an administrative domain (ID) based on the administrator’s Cisco Certified Access Point name, and we’ll give our domain a smaller name in order to better distinguish it from other managed/wireless/static router domains. The MAC addresses of your network equipment and routers should also be unique.
We’ll also create a WAN-specific ip address, which will have a 10.x.x.x subnet mask. The DHCP server is also off as it will be used to assign IP addresses to client devices, while also using resources as SD WAN for this, you can check more about these networks here.
IPDefaultAddress=”10.0.0.1″ #…
Now we’ll turn on WAN bridge for the WAN user.
EnableWANBridge=yes #…
You’ll see the following message appear in the DHCP server configuration dialog:
192.168.1.1:
Change the MAC address to the one in your router, and enter the new address in the Cisco WAN bridge interface config.
#cisco-edit-wlan-bridge MAC address MAC addr MAC=”addr”
When you are done creating the admin password, assign the administrative password to the device. To do this, use the Cisco WAN bridge wizard.
If you need more information about the WAN configuration, see Cisco WAN Bridge
Implementing 802.1Q on the managed/wireless infrastructure
Managed/wireless routers have existing firewall configuration and license rules to stop unauthorized access to the managed/wireless switch. The WAN bridge service performs similar functions in this scenario.
There are three important steps you’ll need to undertake to enable 802.1Q on managed/wireless routers.
Import a database from an R3 switch
This exercise requires that you open a port from R3 (virtual router) to the interface on the managed/wireless router. R3 might have firewall rules against incoming connections to the firewall, so you’ll need to use tools such as fiddler on either a Unix-like system, or portsnap to create a firewall rule to allow network traffic.
